Your environment or ours. Self-hosted, air-gapped or hosted.
Discover it. Measure it. Govern it. Build it responsibly.

The Shield360 AI Control Plane

Every AI call, on the record.

What AI cost, who ran it, what data it touched and what was stopped — one record, in your environment or ours.

app.shield360.ai/demo Demo recording
Recording of the live public demo, unedited. Northwind Demo Co is fictional; every figure is synthetic.

Two ways to use Shield360

Your company’s AI, or your product’s.

One platform, reached two ways. Govern how your people use AI, or monitor the AI you ship to customers.

Enterprise & business

Govern your company’s AI use

Who it is for
Security, finance, compliance and AI governance teams.
How data arrives
From the collector on each computer, the browser extension, coding-agent hooks, the optional AI proxy and vendor billing.
What you install
The collector on macOS, Windows and Linux, and the extension in managed Chrome and Edge.
What you see
Shadow AI and spend by person, guard events, one enforcement policy, the AI inventory and compliance controls.

See the enterprise platform

SaaS & AI builders

Monitor the AI in your product

Who it is for
Teams building AI into their own product or service.
How data arrives
From your apps, through the Shield360 SDK for TypeScript, Python, Go or .NET, or any OpenTelemetry exporter.
What you install
Nothing on employees’ computers. The SDK goes in each app and sends with your Shield360 API key.
What you see
Traces, exceptions, cost and alerts for each app, guard decisions, prompt-injection evaluations, and your apps in the AI inventory.

Shield360 for AI builders

Your AI system of record

Every AI tool is a cost, a risk and a record.

Shadow AI, personal accounts, coding agents, agents calling tools, spend no invoice explains: one record of all of it, with no proxy and no root certificate.
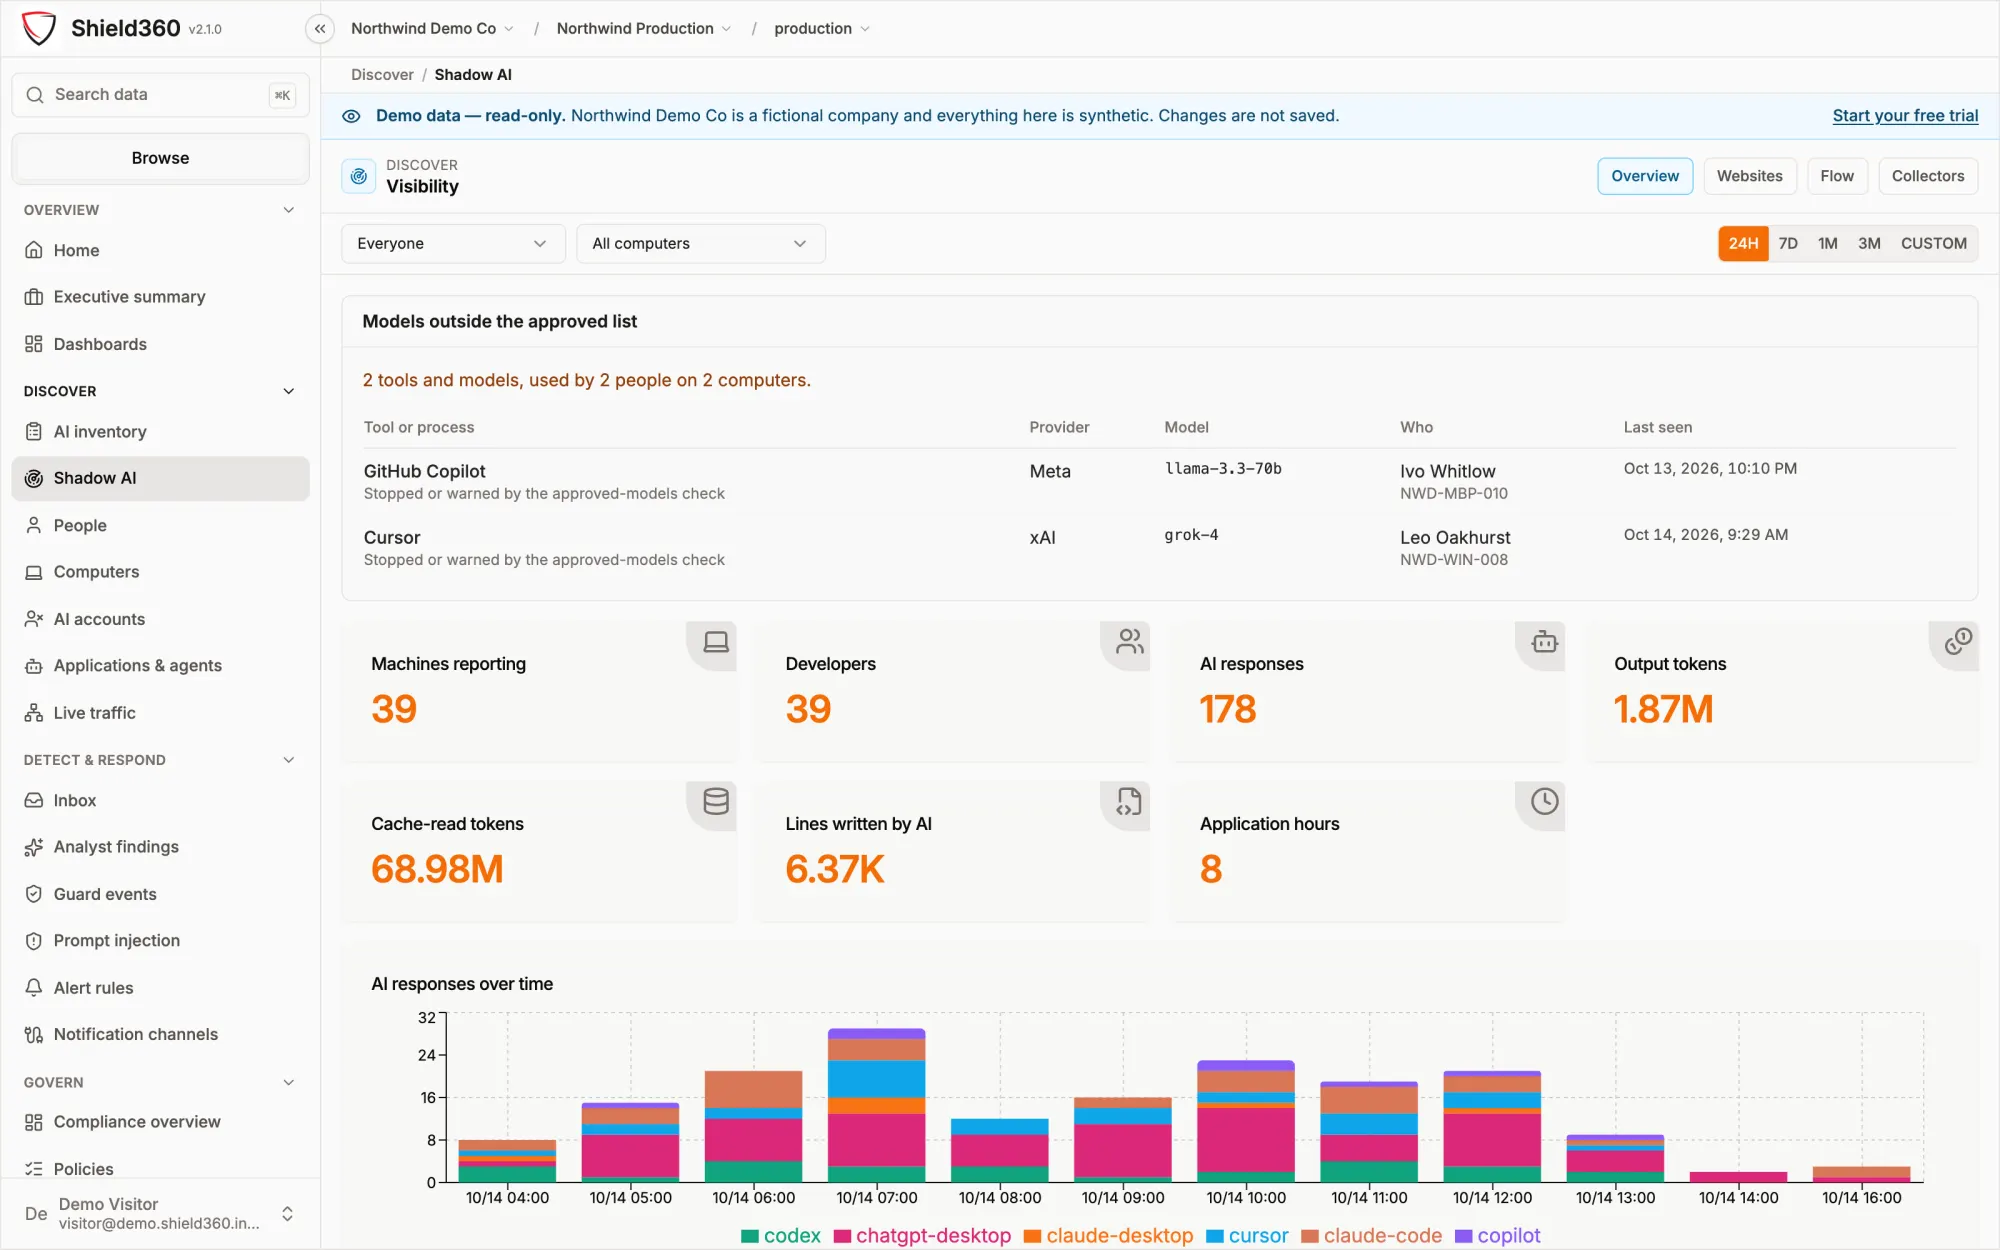
Walk every screen

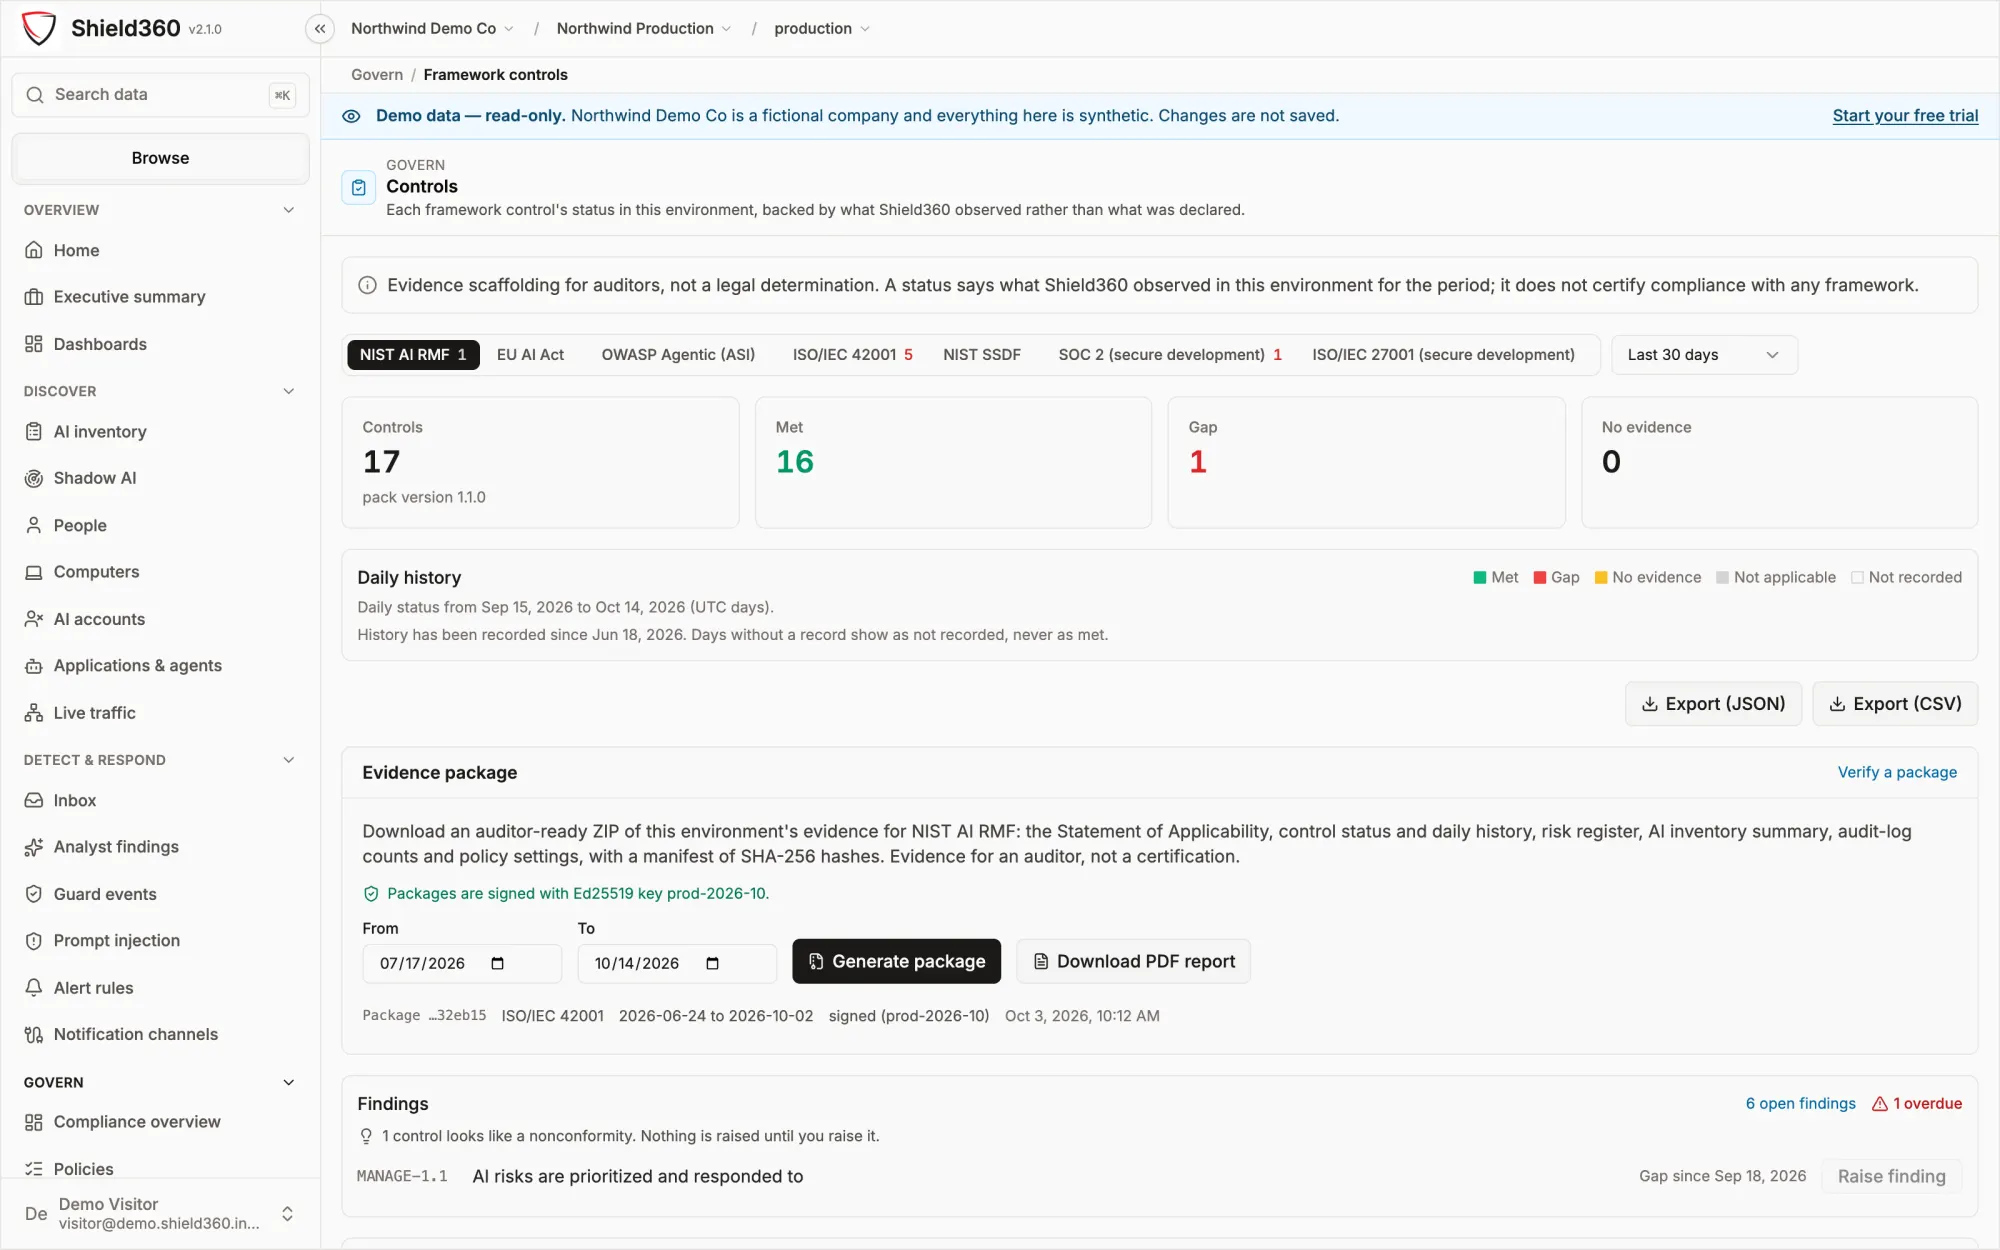
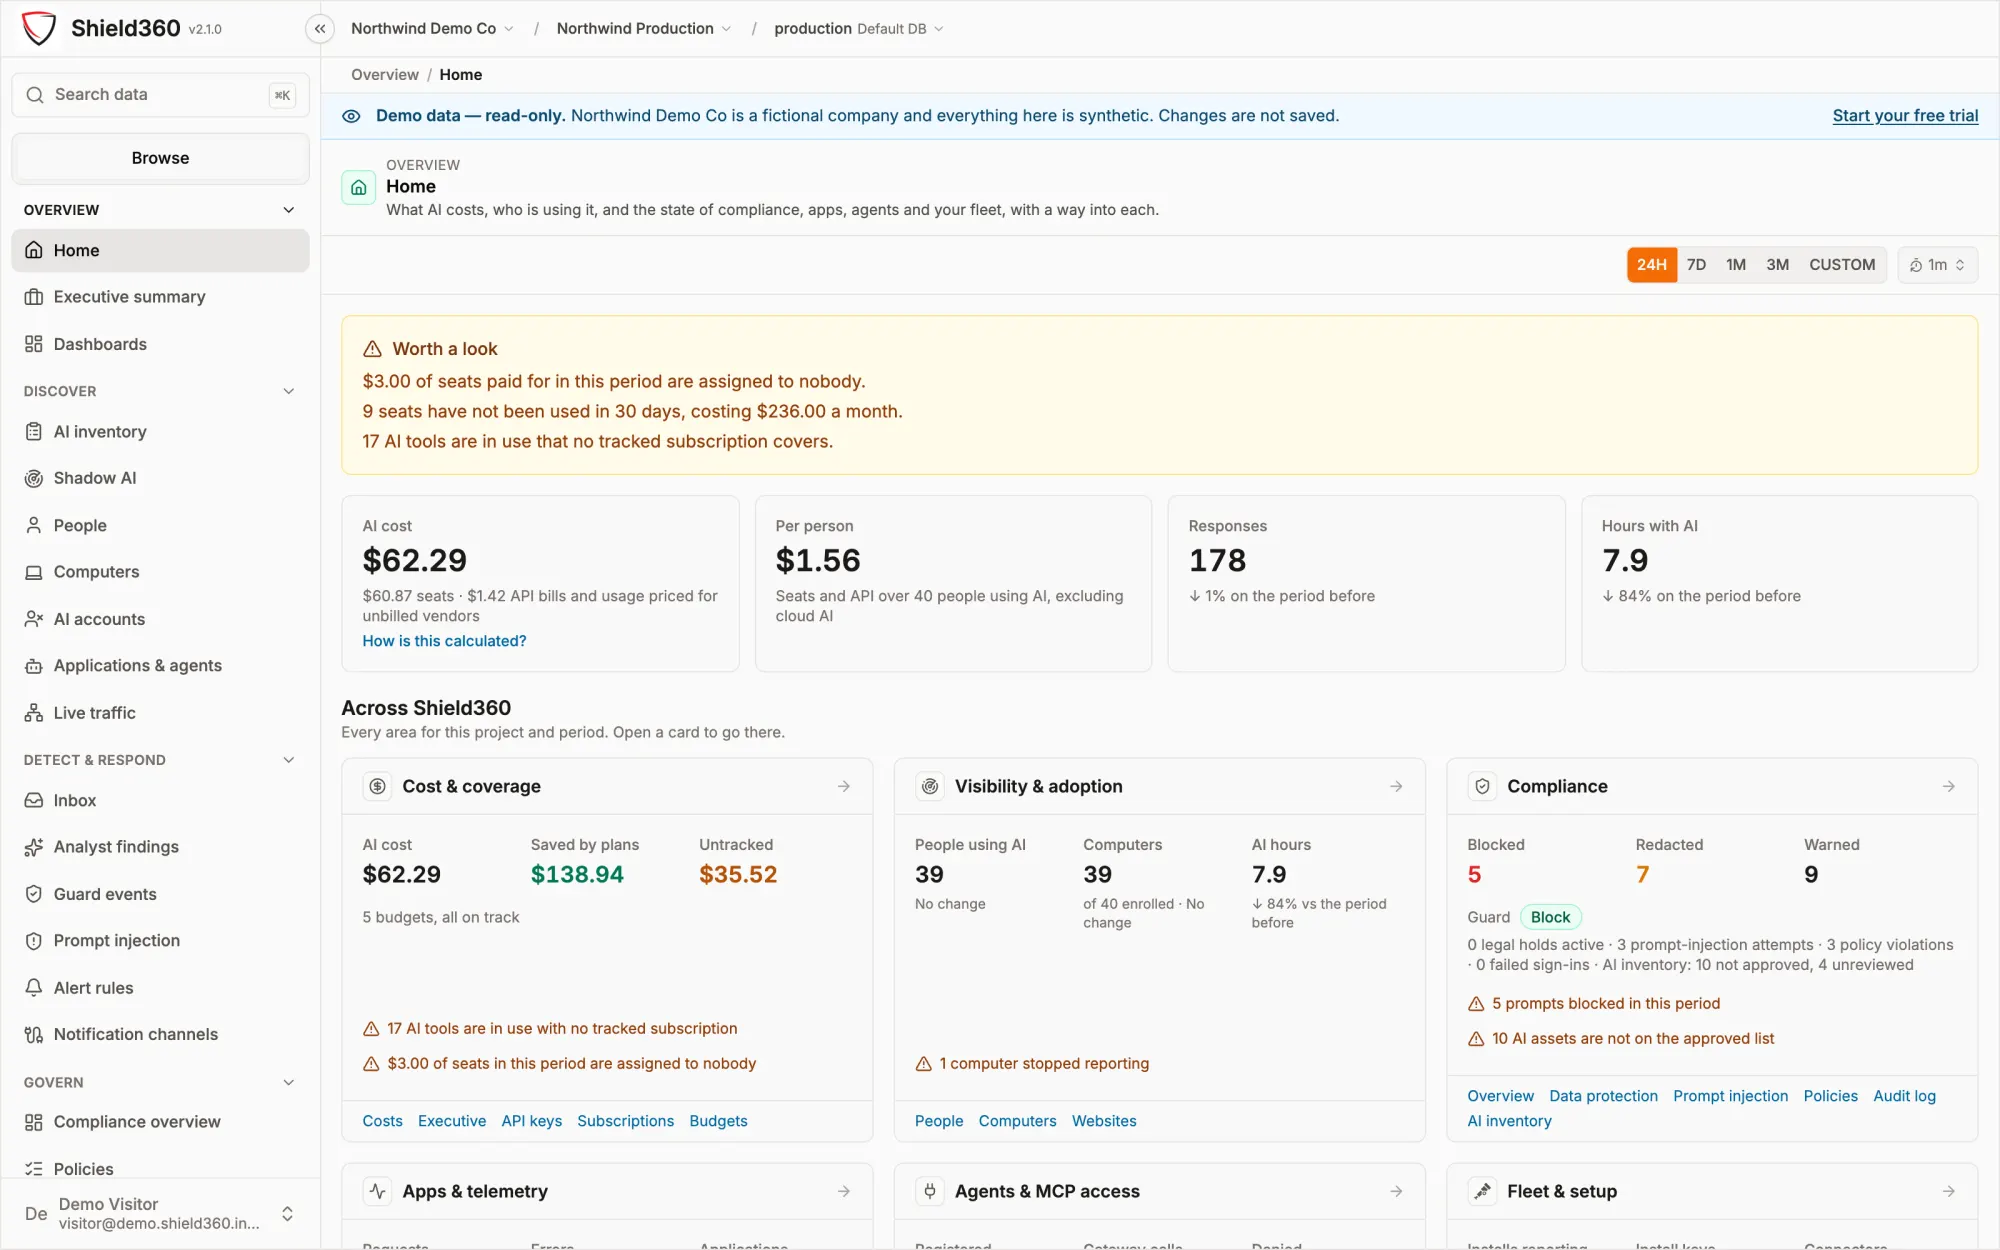
app.shield360.ai/demo · HomeDemo capture
The Shield360 Home screen in the public demo: AI cost, cost per person, responses and hours with AI, then cards for cost and coverage, visibility and adoption, and compliance.
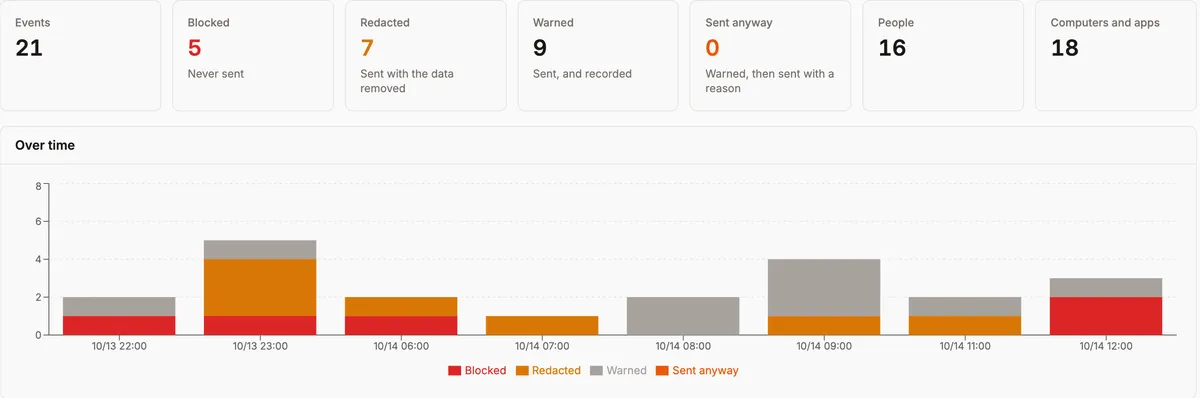
Detail of the Guard events screen: 21 events, of which 5 blocked, 7 redacted and 9 warned, over time.

Unedited captures of the public demo. Synthetic data.
Four modules, one record

Wherever AI reaches, keep the record.

Four modules on one dataset, each available alone. Start with your biggest AI challenge.

Security module · Discover it

See every AI tool in use, and keep sensitive data from leaving.

Shadow AI by person and computer, with no root certificate and no proxy changes. Prompts carrying secrets or personal data are warned on, masked or blocked.

Why it matters:

No root certificate Discovery needs no certificate and no proxy changes.

One policy The browser extension, the AI proxy and coding-agent hooks read the same organization-wide policy.

Explore Security resources:

Finance module · Measure it

Put a name on every AI dollar.

Spend by person, machine, tool and model, from the invoice where a bill is connected and marked as an estimate where not.

Why it matters:

Untracked spend, shown Spend no plan explains gets its own line, never hidden in another.

Paid for, unused Seats nobody holds, or nobody used in 30 days, are listed as exactly that.

Explore Finance resources:

Compliance module · Govern it

Evidence an auditor can check, recorded before they ask.

Control status for ISO/IEC 42001, the EU AI Act and NIST AI RMF from observed evidence, kept daily. Evidence, not a certification.

Why it matters:

38 of 38 ISO/IEC 42001 Annex A controls, each with a Statement of Applicability entry.

Never edited The audit log records reads as well as changes; the database refuses to update or delete it.

Explore Compliance resources:

Developer module · Build it responsibly

Let teams build with AI, inside the limits the company set.

Coding-agent analytics for Claude Code, Cursor and Codex, data guards, and approved models enforced at the AI proxy.

Why it matters:

By tool and repository Lines written by AI are reported by tool and repository, never as a measure of a person.

Approved models only The AI proxy can warn on, or refuse, a model outside the approved list.

Explore Developer resources:

Enforcement points

One policy. Five places it is enforced.

Off, warn, mask or block per kind of sensitive data, from one organization-wide policy.

Detected everywhere. Enforced where you choose.
  1. Person → AI website

    Browser extension

    Checks prompts on eleven AI chat sites; allows, warns or blocks the rest.

    How it works
  2. App → model API

    AI proxy

    By base URL, no root certificate. Approved providers and models only.

    How it works
  3. Developer → coding agent

    Coding-agent hooks

    Claude Code, Cursor and Codex: prompts, secret files, injection.

    How it works
  4. Agent → tools and data

    MCP gateway

    A token per agent; deny-by-default grants, read on every call.

    How it works
  5. Your app → before the model

    Guard check API

    Your app asks before it calls a model. The text is never stored.

    How it works
Where it stops

No TLS interception: internal apps are covered through the AI proxy or the guard API. Other AI use is still discovered and reported.

The platform

Every AI control, in one product.

Each a working area of the product today, not a roadmap item.

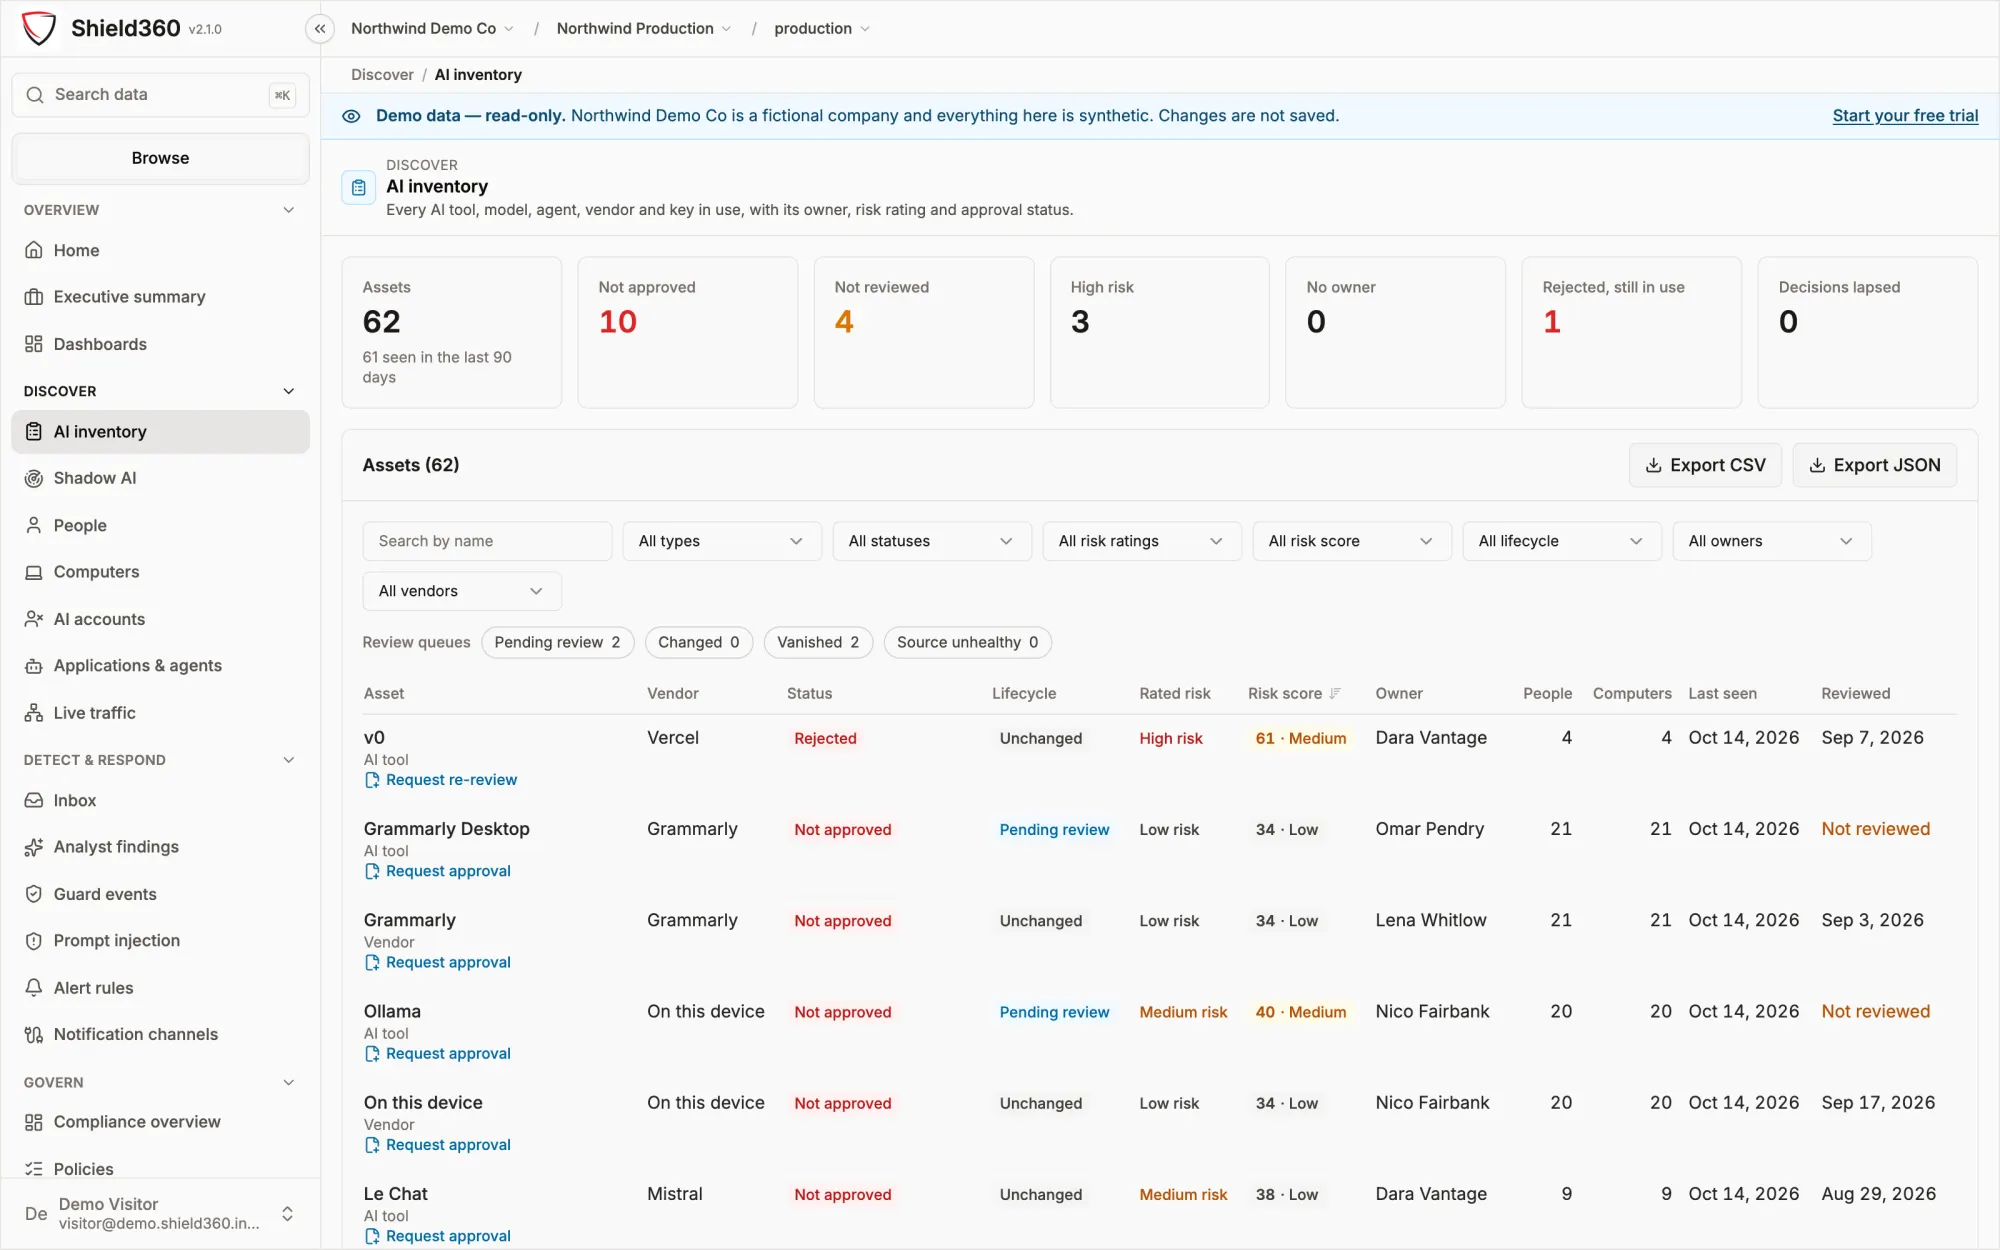
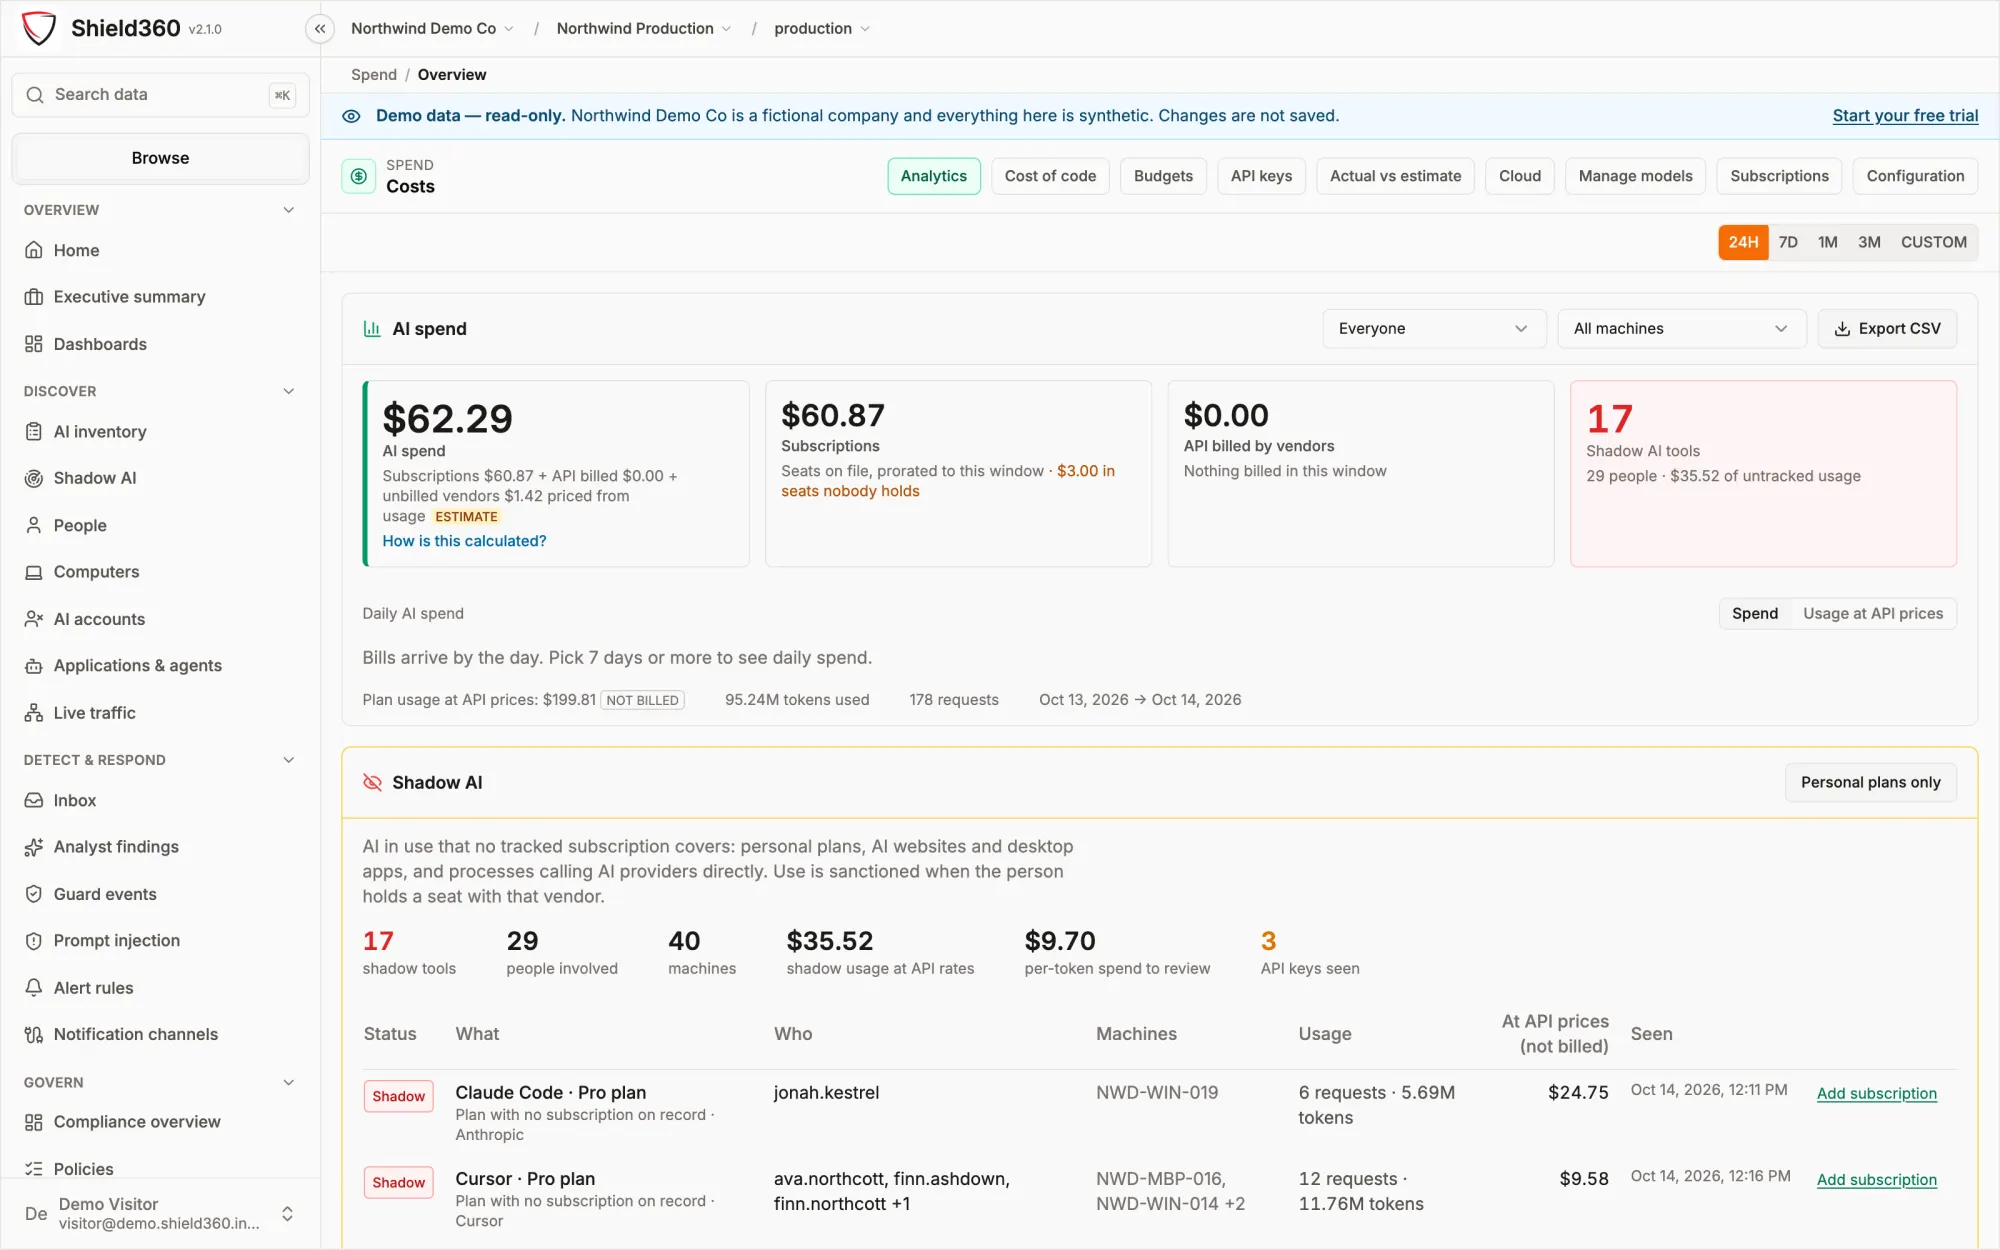
app.shield360.ai/demo · AI inventoryDemo capture
The AI inventory in the public demo: assets by type, vendor, status, lifecycle, risk rating, owner, people and computers, with filters and CSV and JSON export.
AI inventory, an unedited capture of the public demo. Synthetic data.
Deployment

Your environment or ours.

The same software either way: you choose where the data lives.

Self-hosted · air-gapped

Installed in your environment

  • Docker, or Kubernetes with manifests we provide
  • Your own ClickHouse and Postgres hold the data
  • Air-gapped: no licensing call-home, no telemetry back to us
Hosted SaaS

Hosted and operated by us

  • Each organization gets its own database, not a shared table
  • Sign-in federates to your own identity provider over OIDC
  • A hosted pilot can move in-house for production

Compare the deployments side by side

Built to be checked

Answers that hold up under review.

Built into the product, not left to a setting.

No root certificate And no proxy changes, on any machine.

7 years Every block and warning, kept by the database.

Tamper-resistant Audit log entries can’t be edited or deleted.

Safe by default If the policy can’t be reached, nothing extra is collected.

Every retention horizon What leaves a machine

Questions

Asked before a pilot gets approved.

The rest are answered in the documentation

Is Shield360 installed on-premises, or is it SaaS?

Either. Install it in your own environment — on Docker, or on Kubernetes with manifests we provide, against your own ClickHouse and Postgres, including fully air-gapped — or use the hosted service, where each organization gets its own database. Both are the same software with different configuration, so a hosted pilot can move in-house for production.

Does Shield360 sit in the path of our AI traffic?

Not unless you choose to put it there. The collector installs no certificate, changes no proxy setting and opens no listening socket. It reads files the AI tools already write and tables the operating system already keeps, then sends what it found outbound over TLS. The one part that does sit in the path is the optional AI proxy, and only for applications you point at it by base URL. It needs no root certificate, and traffic you do not route through it never reaches it.

Without a proxy, how can it block anything?

Data protection runs at the point of use. The browser extension, in managed Chrome and Edge, allows, warns about or blocks the AI sites on its list, and on eleven AI chat sites, ChatGPT, Claude, Gemini and Microsoft Copilot among them, can warn about, mask or block a prompt carrying a secret or personal data before it is sent. Hooks inside coding agents can warn or block. Where you want enforcement on the wire, the optional AI proxy applies the same policy and can refuse models outside your approved list, and your own applications can ask the guard check API before they send text to a model. One organization-wide policy drives all of them.

Can it read our prompts and the model's responses?

Data protection reads a prompt before it is sent, so it can act on it. Storing it is a separate choice, and it is off by default: no prompt, response or tool content is kept unless an administrator turns that on. What is always kept is the model, token counts, cost, the guard's decision and the kinds of sensitive data found. An environment can only store less than its organization, and secrets are always scrubbed from anything stored.

How is Shield360 priced?

The hosted service has published plans: Free, Team and Business, each with apps, computers, spans and retention included, and add-ons for more. Paid plans start with a 14-day trial, no card needed. See pricing. Self-hosted and air-gapped deployments are Enterprise: book a briefing and we’ll price it with you. Or start free on the hosted service.

Ready for a conversation?

Bring one AI question. Leave with a plan.

A working session on the live product. We say plainly what Shield360 can and cannot answer.